Legacy websites are a constant source of vulnerabilities. In a fit of excitement, a team commissions a service and then never bothers updating it. Quite often the original owners leave the business and there's no-one left who remembers that the service exists. So it sits there, vulnerable, for years. The [REDACTED] website had a subdomain which was running KANA's IQ software which was last…
Continue reading →

Bit of a boring write-up, but here we go. Taxi app Gett had a content injection flaw in its search function. By searching for an HTML string, it was possible for an attacker to add links or images to a page. It was really hard to contact them - but the threat of media attention sprung them into action. For example, searching for a specially crafted string meant that an arbitrary SVG could be…
Continue reading →

The UK faces an epidemic of telephone scams. Fraudsters are constantly calling people up pretending to be their bank. But how can you be sure the number displayed on your screen in genuine? You can't. The telecom system is hopelessly insecure and shouldn't be trusted for anything more complicated than dialling the speaking clock. Barclays bank knows that customers are worried about this. So…
Continue reading →
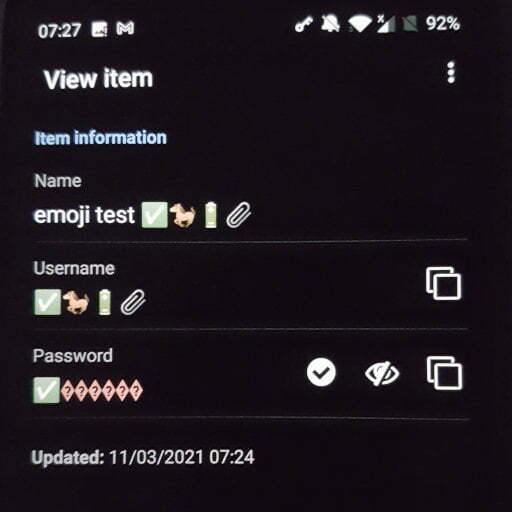
Let me start by saying that Emoji Passwords are probably a really daft idea. I want to use emoji in my passwords. They're easy to type on a mobile keyboard, easy to remember, and a lot more fun than boring ASCII characters. Let's go with ✅🐎🔋📎 (As close as possible to Correct Horse Battery Staple) I use BitWarden as my password manager. It saves emoji passwords into its database, but has troub…
Continue reading →
Once in a while, big companies suggest that the answer to abuse is to ban anonymity and institute a Real Names policy. This time, it is Google's turn. They think that critical software should only be authored by people with "real names". I don't want to go into whether this is a good idea or not. Nor philosophical discussions of what a "real name" is. I want to discuss how this would work…
Continue reading →
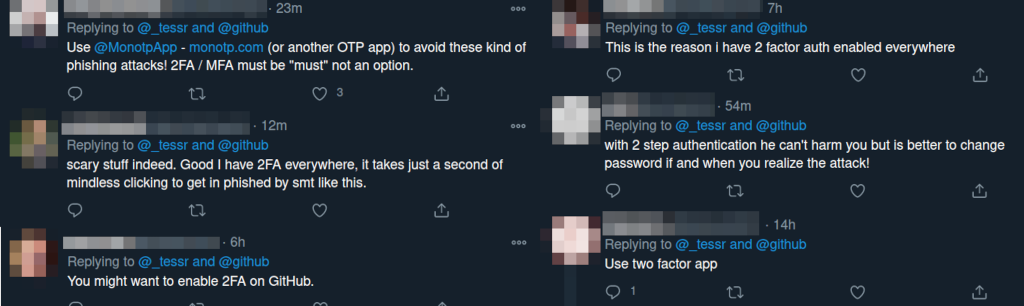
Another day, another high-profile website cloned to phish credentials. Tess Rinearson@_tessrIs this a phishing attempt? Goes to "githubverification.com" and asks for username and pw (if so, it nearly got me!) /cc @github pic.x.com/jgt4oNvjF2❤️ 2,243💬 111🔁 016:12 - Sat 16 January 2021 In the replies, you’ll see lots of techbros saying “this is why you should switch on 2FA people!!!” Except, an…
Continue reading →

(For the new reader, there is a famous essay called Falsehoods Programmers Believe About Names. It has since spawned a long list of Falsehoods Programmers Believe About....) Everyone has fingerprints! The BBC has a grim tale of a family with a genetic mutation which means they have no fingerprints. It details the issues they have getting official ID. In 2010, fingerprints became mandatory for…
Continue reading →

A curious little data leak, but one I struggle to care about. Perhaps useful for a bit of fingerprinting? Websites can access your system's camera and microphone. That's how modern video conferencing works in the browser. In an effort to retain user privacy, the browser asks the user for permission to use the camera and mics. No audio or video will be sent until the user agrees. But some…
Continue reading →

Without your permission, or even your awareness, tech companies are harvesting your location, your likes, your habits, your relationships, your fears, your medical issues, and sharing it amongst themselves, as well as with governments and a multitude of data vultures. They're not just selling your data. They're selling the power to influence you and decide for you. Even when you've explicitly…
Continue reading →

I hate the Internet of Things. It's a load of overpriced junk, which abuses your privacy and demands a monthly fee in return. That's why I was pleasantly surprised to see this fall out of the eufyCam 2C box. There's no monthly fee. The recordings stay in your home. The batteries last for ages. I can get on board with this! The package costs around £220 (discount of £40 if you use my code) and …
Continue reading →
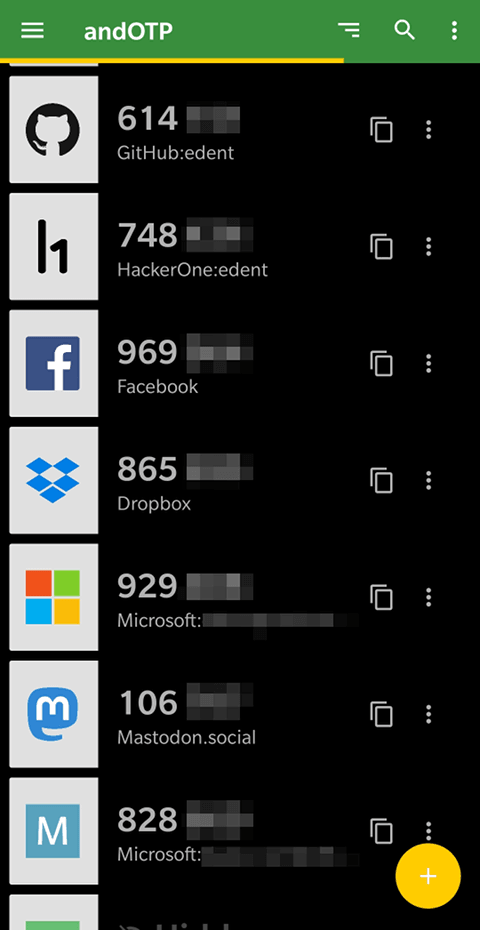
Last year, when doing some digital spring-cleaning, I realised that I had 800 different passwords. I tried going through them, removing long-dead websites, closing old accounts, and deleting anything incriminating. I now have 891 accounts. Arse. I also went through my 31 different 2FA accounts. Getting rid of old employers' email tokens, failed crypto wallet providers, Club Penguin etc. I…
Continue reading →
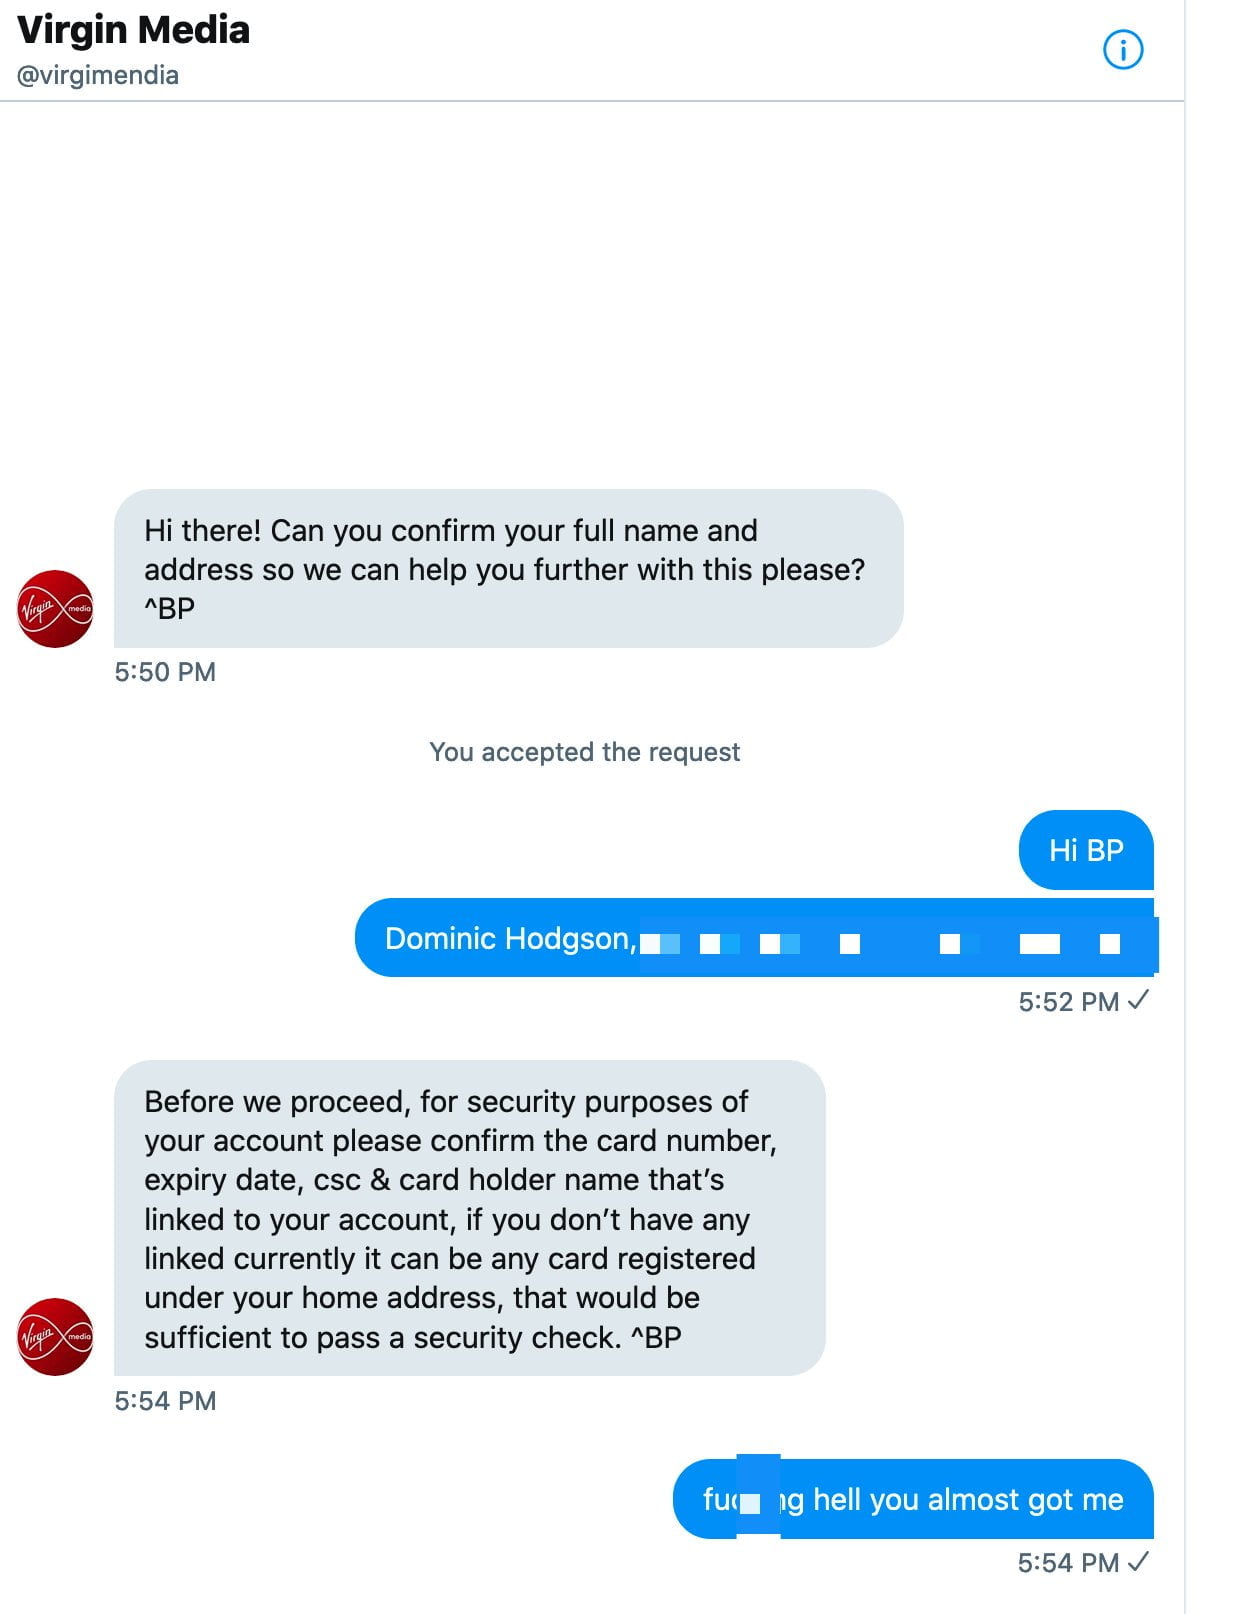
My mate Dom was moaning to his ISP on Twitter. They sent him a private message so they could look into his account. Blimey! Thankfully, that was a pretty brazen and inept attempt at phishing. Anyone asking for all your card details like that should set the alarm bells ringing. Of course, phishers often target credulous people who don't understand that they're being scammed. By sending an…
Continue reading →