It is a truth universally acknowledged, that an ISP in possession of a good Internet connection must be in want of a customer. One would think that, in these capitalist times, ISPs would compete over who could provide the fastest speed, the best service, and the lowest price. Sadly, in the UK, our ISPs seem to compete on who can be slightly less awful than each other. Last night, I did what…
Continue reading →
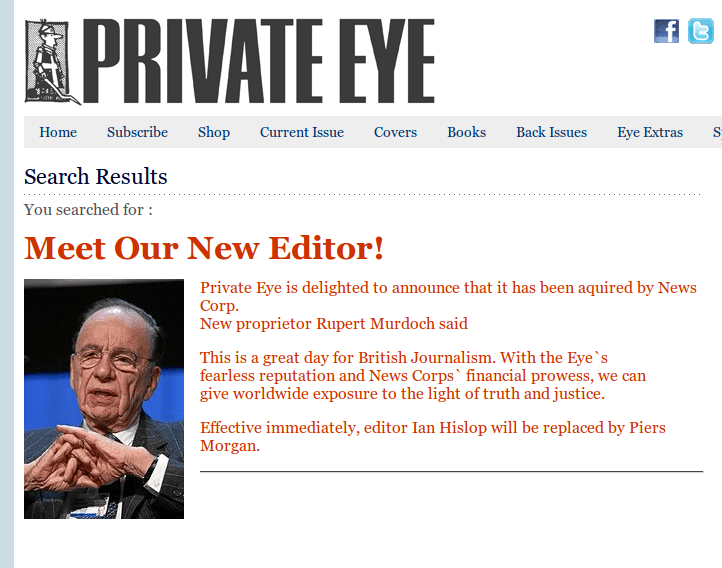
Private Eye is the only "Dead Tree" publication I buy. I think its satire misses the mark more often than not - but its investigative journalism and general muck-raking are second to none. The Eye has reluctantly been drawn into the digital age. It has a piss-poor website run by the sort of "tired and emotional" gnomes who struggle with concepts like sanitising user input. EXCLUSIVE Push…
Continue reading →

The Citizens' Advice Bureaux have just released a real-time view of what people are searching for on its site. It's heartbreaking. Tom Loosemore@tomskitomskiInteresting new digital stuff emerging from @CitizensAdvice display-screen.cab-alpha.org.uk <-- uncomfortable, messy, visceral reality @mikedixonCAB❤️ 8💬 3🔁 010:03 - Tue 21 October 2014 who supplies my electricity why do some children become…
Continue reading →

Her Majesty’s Inspectorate of Constabulary (HMIC) are the police who police the police. As the Police policers you'd expect their website to be copper-bottomed. That they would detect anything amiss when inspecting their thin blue links. Mind you, some web developers are a law unto themselves. Yeah, yeah, these puns are unbearable. Fine. Whatever. Amusing photo by kind permission of the i…
Continue reading →

Just a short usability / security post. Hopefully, you're all using Two-Factor Authentication on your important sites. As well as a username and password, you've also got to enter a one-time code. Usually it is generated by an app, or sent to you via SMS. Each code can only be used once - which makes it all the more curious that, after a few logins, Twitter's website looks like this: Now,…
Continue reading →

Imagine, just for a moment, you suspect that a friend of yours is a criminal. Perhaps they are running an illegal proxy, or hosting a search engine, or maybe criticising a dangerous cult, or even taking suspicious photographs. These are all - apparently - within the remit of The City Of London Police. Better report such heinous crimes to them. As a high-tech policing unit, they encourage you…
Continue reading →

Running a website is hard. Let me clarify - setting up a website is dead simple - keeping it running and updated is tricky. Now, for some of us, it doesn't really matter whether our sites live or die. But for big companies like McAfee it's not simple to switch off a site - especially when they've promised to keep it running in perpetuity. For some reason, the world's largest computer security …
Continue reading →
A (very minor) privacy issue I found with the iTunes API - disclosed on 7th April. Apple provide an API to allow users to search the iTunes store. Let's suppose that a user wishes to search for Music Videos from The Beatles. The search itself is performed over HTTPS. https://itunes.apple.com/search?entity=musicVideo&term=beatles This means that anyone sniffing the connection won't see what…
Continue reading →

A few months ago, I was attending the National Hack The Government event. I was showing off some of the work I had been doing on "The Unsecured State" - looking at *.gov.uk website security. I was chatting to an envoy from the Food Standards Agency who was eager to hear more about what I'd discovered. "Oh," I said, "It's pretty easy. Let's take a look at your website. If I were to type some…
Continue reading →

As part of my "National Hack The Government" win, I was awarded 100 DogeCoin! Although not my first foray into the exciting world of CryptoCurrencies, I'd never received DogeCoin before. I decided to set up an online wallet to temporarily store my loot while investigating more secure options. More or less at random, I went with DogeAPI.com. After registering, I received this email. Let's…
Continue reading →

We're all changing our passwords in the light of Heartbleed, right? Good! If you are a developer or designer, I want to explain to you exactly how not to create a password dialogue box for your users. We're all used to seeing this: Input password: Change Password This is incorrect! Why? Because it leads to this? Input password: Change Password ERROR! Your password must be longer than …
Continue reading →

This is part 5 of a series of blog posts looking at the security of the UK Government's web infrastructure. The primary cause of the vulnerabilities I've exposed over this series is abandonment. In a flurry of excitement a website is commissioned and created. Then, as time wears on, people begin to drift away from the project. Job titles change, people are reshuffled, and senior…
Continue reading →