I want to discuss a (minor) antipattern that I think is (slightly) harmful. Lots of websites use large Javascript libraries. They often include them by using a 3rd party Content Delivery Network like so: <script src="https://cdn.example.com/js/library-v1.2.3.js"></script> There are, supposedly, a couple of advantages to doing things this way. Users may already have the JS library in their…
Continue reading →

Given a social media user's username, how do you get a picture of their avatar? I always used avatars.io - but sadly that service has bitten the dust. So I've switched to unavatar. It's dead easy to use. https://unavatar.now.sh/twitter/edent will return @edent's avatar. You can use GitHub, Facebook, Gravatar, Instagram, Telegram, YouTube, SoundCloud, and a couple of other providers. Simple…
Continue reading →

This is the latest of my many terrible lockdown-induced ideas. I'm saving money on commuting. So I'm spending it on tech-crap I really don't need. I bought a new laptop sticker. Anyway, enough waffle, here's the end result: This uses 2-frame lenticular printing. History No browser supports the <blink> element any more. It used to make text blink. It was a silly idea that got out of…
Continue reading →
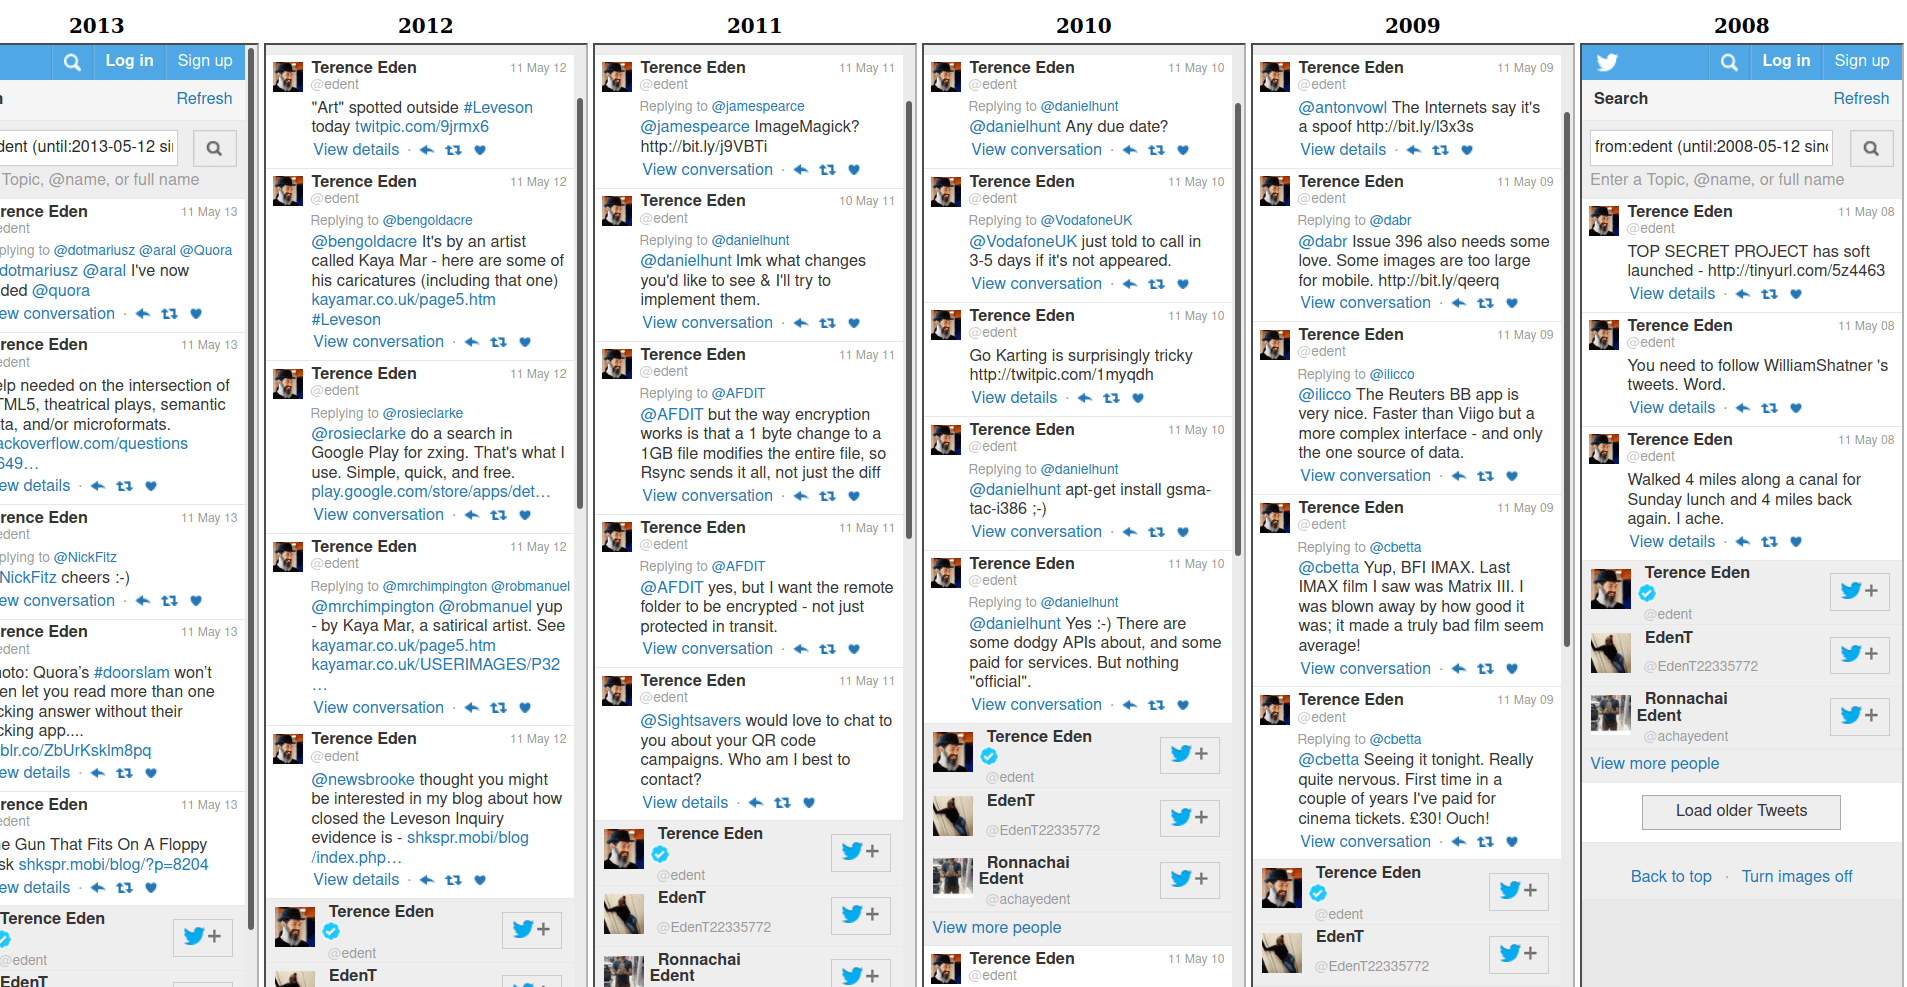
I wanted to see what I was Tweeting on this exact day last year. And all the years before. So I built a website! It's a disgusting hack, and I'm truly sorry for unleashing it on you. Using the API You can't. The Twitter search API only goes back 7 days. This whole idea would be much easier if I had access to the Premium API. But! The Twitter website has no such restrictions. Advanced Search …
Continue reading →

My Chinese takeaway delivery was late. Very late. I flipped open the confirmation email sent by Just-Eat to double-check I had all the details correct. At the bottom was a "click to call" link. Hurrah! I clicked dial, and this is what filled my screen: An absurdly long phone number. Bemused, I went to inspect the link I'd clicked. This is what it showed: The tel: URl scheme is brilliant. …
Continue reading →

My friends, and former employers, at the Government Digital Service have written a spectacularly good blog post "Making GOV.UK more than a website". In it, they describe how adding Schema.org markup to their website has allowed search engines to extract semantic content and display it to a user. For example, the "Learn to drive" page has content which can appear directly in a search engine: …
Continue reading →
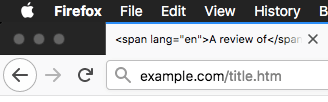
How much do you know about the humble <title> tag? It has been there since the earliest HTML specification. The 1995 spec says: There may only be one title in any document. It should identify the content of the document in a fairly wide context. It may not contain anchors, paragraph marks, or highlighting. Remarkably little has changed in the intervening decades. The modern HTML5 spec…
Continue reading →

(This isn't really a security issue, although I've disclosed it to the Twitter team.) "Fuzzing" is a computer science term which means "sending weird data into a program and seeing what happens." It's a useful way to see how your code can break in new and unexpected ways. It's particularly good at showing what a website's search engine does when it is confused. For example, here's a fairly…
Continue reading →
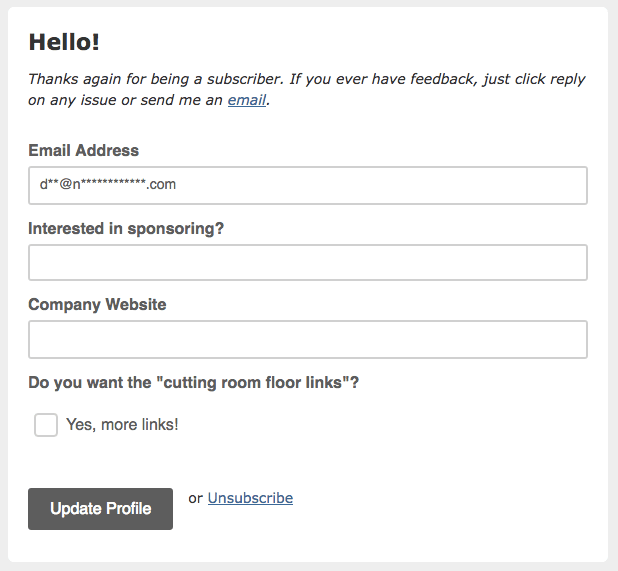
An annoying privacy violation from leading email newsletter company MailChimp. Responsibly disclosed on 2017-12-04. When you click a link on a webpage or an email, your browser opens up that link and sends the newly visited webpage a Referer Header. (The misspelling is a historical artefact.) This says "Hello new site, I was referred here by this previous website." This has some privacy…
Continue reading →

This is a sketch of a proposal for a new HTML element to simplify displaying maps on a website. I'd like your comments and criticisms before I submit it. This is born out of my frustration of using different JavaScript mapping solutions - my phone has a mapping app, why do I need to share my location with a website and their mapping provider? At the moment, if I want to use Google Maps, or…
Continue reading →

We've all been faced with this screen, right? You haven't logged in to a website for a while, so it prompts you to change your password. sigh Annoying but probably necessary. The problem was, every time I tried to change my password, it told me that my old password was invalid. The one that I'd just used to log in. I use the incredible LastPass Password Manager - so I knew I wasn't typing…
Continue reading →

Update! I now have an XSS which is only 18 characters! Here's a fun little game for all the family! What is the minimum number of characters required to perform a successful XSS attack? Let's take an entirely theoretical example - suppose we have a site which echos back user input without sanitising it. So a search for " <em>" turns the whole page italic. ahem A hacker might think, "Hurrah! …
Continue reading →